UnrealIRCd Vulnerability CVE-2026-114713: Ordinary Users Can Run Server Commands, Has Been Exploited
By Tim APIPedia, Tim Engineering APIPedia · Published · Updated · 9 min read
The UnrealIRCd vulnerability CVE-2026-114713 allows ordinary users to execute server commands and has been exploited. This is how to check, hot-patch and detect it.
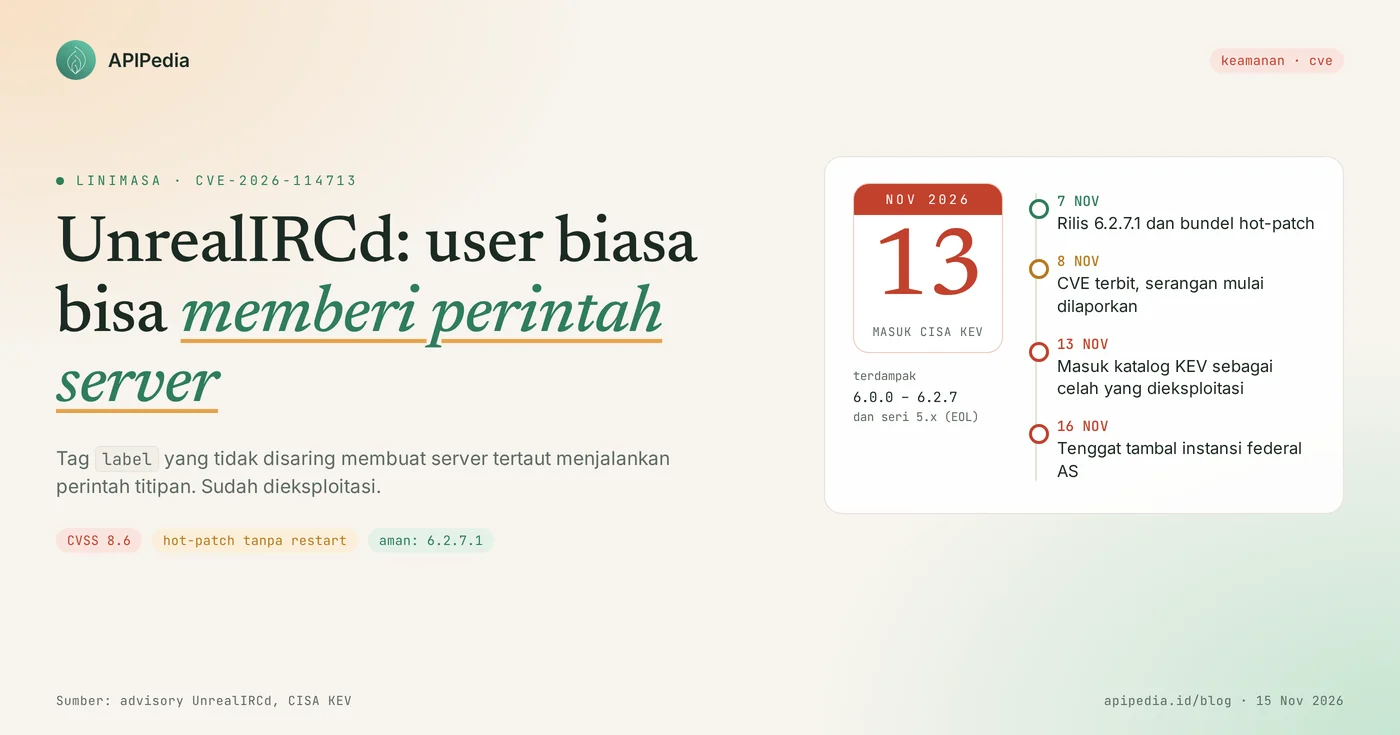
CVE-2026-114713 is a command injection vulnerability in UnrealIRCd that allows ordinary users to execute commands with server authority or IRCOp, with a CVSS 3.1 score of 8.6. Versions 6.0.0 through 6.2.7 are affected, a fix is in 6.2.7.1 (November 7, 2026), and CISA listed them in the Known Exploited Vulnerabilities catalog on November 13, 2026 because they were exploited.
UnrealIRCd is one of the most widely used open source IRC servers, including by communities, campuses, internet cafes, and teams that run their own chat networks. The maintainers call this the most critical issue discovered in UnrealIRCd in the last 15 years. This article explains how it works, who is affected, safe versions, check scripts, how to install hot-patches without restarting, and how to look for signs of abuse.
Quick summary
| Items | Details |
|---|---|
| CVE | CVE-2026-114713 |
| Product | UnrealIRCd, module labeled-response (loaded by default) |
| Gap type | Interserver command injection due to separator characters not being neutralized (CWE-140) |
| CVSS score 3.1 | 8.6 (high), over the network, no access rights, no user interaction |
| Impacted version | 6.0.0 to 6.2.7, as well as the unsupported 5.x series |
| Safe version | 6.2.7.1, or series 6 which has hot-patch bundle-20261107 installed |
| Attack conditions | An IRC network with two or more linked servers |
| Status | Actively exploited, entered CISA KEV November 13, 2026, US federal deadline November 16, 2026 |
How does this UnrealIRCd loophole work?
This loophole works because module labeled-response copies the contents of the client post's tag label into the reply without filtering out the separator characters. As a result, the insertion in the tag can be read as a new command line by other servers on the same network.
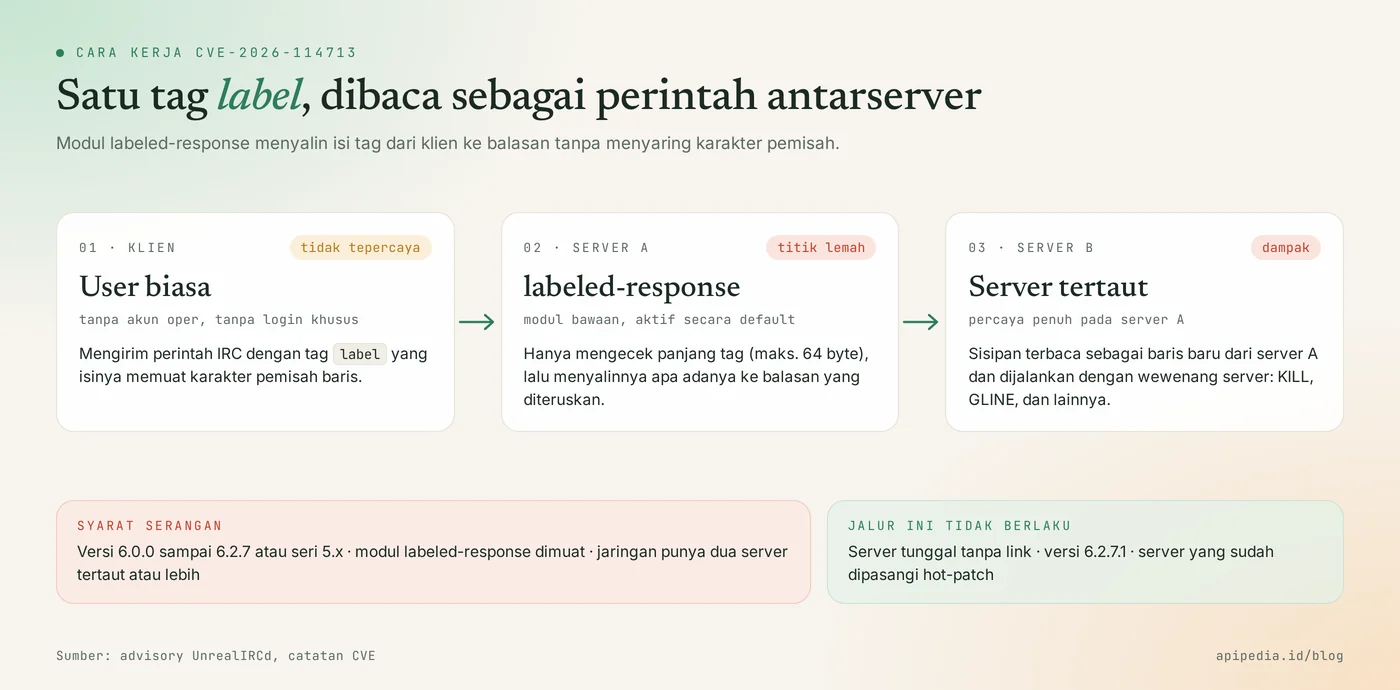
The order is like this:
- Modern IRC clients may attach the tag
labelto their commands. The server returns that tag in the reply so the client can match the question and answer. - In the vulnerable version, the server simply checks that the tag is not empty and that it is a reasonable length. The contents of the bytes inside are not checked.
- When the reply is forwarded to another linked server, the insert in the tag is read as a separate line that appears to have been sent by the originating server.
- The receiving server has full trust in the linked server, so the line is executed with the server's authority.
Why do you need two linked servers?
Because the authority that is misused is trust between servers. On a single server without a link, no other server accepts the inserted row, so the server's path of authority does not apply. This article intentionally does not contain examples of attack tags or commands.
Who is affected?
Affected are UnrealIRCd-based IRC networks that meet all of the following conditions:
- Running UnrealIRCd 6.0.0 to 6.2.7, or 5.x series.
- Module
labeled-responseis loaded. This is a default condition, so almost all standard installations meet it. - A network consists of two or more linked servers, for example a hub and a leaf, or a main server and a service server.
- Outsiders can connect as regular users. Attackers do not need a registered account or operator status.
The 3.2.x and 4.x series are not checked by maintainers because they have not been supported for a long time. Assume the series is unsafe and plan a migration.
How serious is this loophole?
Seriously: it scores 8.6, can be triggered by anyone who can connect, and was already used in a real attack the day after the fix was released.
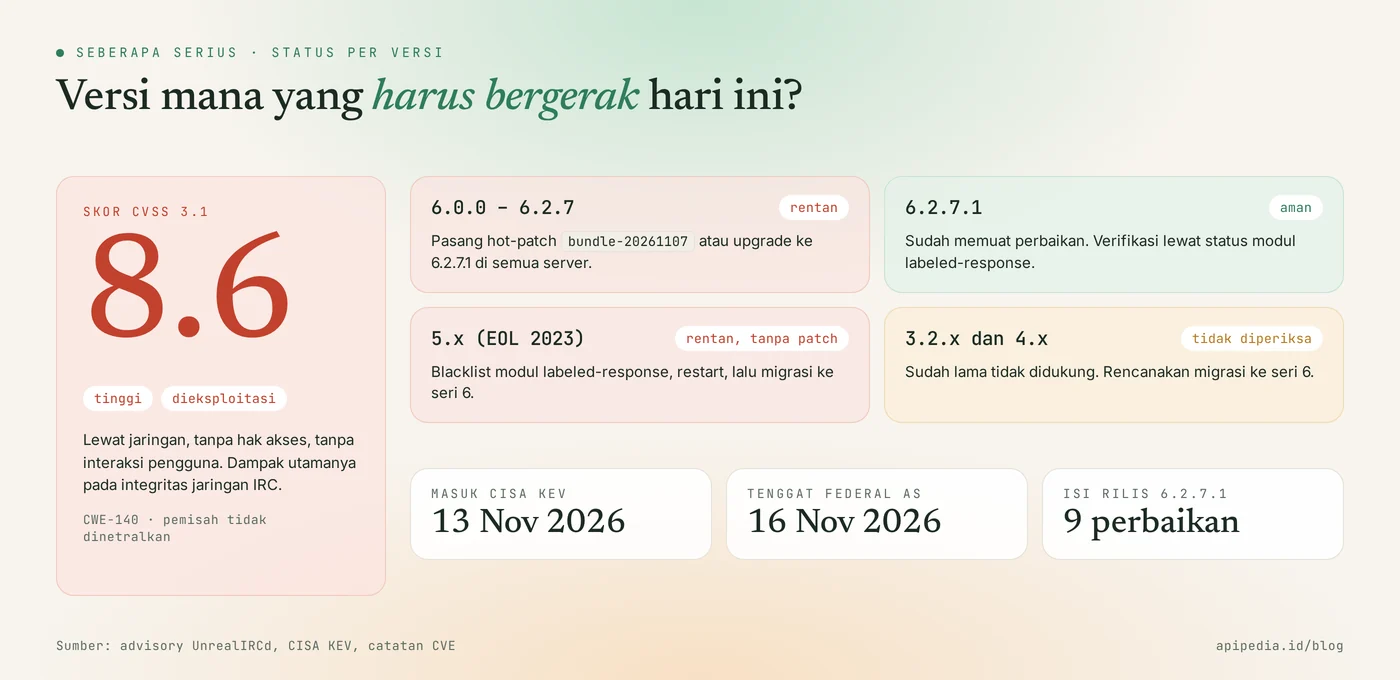
- Real impact: ordinary users can disconnect other users (KILL), ban the entire network (GLINE), and carry out other operator actions.
- November 7, 2026: UnrealIRCd 6.2.7.1 and hot-patch bundle released. This release contains nine fixes, including this vulnerability.
- November 8, 2026: CVE notes are published, and exploit attempts begin to be reported. The administrator said he saw attackers exploiting this loophole on the internet.
- November 13, 2026: CISA adds it to the KEV with a November 16 deadline for US federal civilian agencies.
- The CVSS vector assesses the impact on integrity. In practice, service disruptions also occur when users are disconnected or mass banned.
Which version is safe?
The safe version is UnrealIRCd 6.2.7.1 and above, or series 6 which has hot-patch bundle-20261107 installed.
| UnrealIRCd version | Status | Action |
|---|---|---|
| 6.2.7.1 and above | Safe | Verify module status |
| 6.0.0 to 6.2.7 | Prone to | Install hot-patch or upgrade to 6.2.7.1 on all servers |
| 5.x (end of support July 1, 2023) | Vulnerable, no patch | Blacklist module labeled-response, restart, then migrate to series 6 |
| 3.2.x and 4.x | Not checked | Migration to series 6 |
If UnrealIRCd was installed from a distro package, follow the updates from the package manager. The patched package version number may differ from the official release number.
How do I check if my server is affected?
Check the version number and status of module labeled-response on each server. The following script is read only. The version comparison logic has been tested in the sandbox with mock output for 4.2.4, 5.2.4, 6.0.0, 6.2.7, 6.2.7.1, and hot-patched 6 series.
#!/bin/sh
# Cek paparan CVE-2026-114713 di UnrealIRCd. Hanya membaca, tidak mengubah apa pun.
# Jalankan dari direktori instalasi (misalnya ~/unrealircd) di SETIAP server jaringan.
ver=$(./unrealircd version 2>/dev/null | grep -oE '[0-9]+\.[0-9]+\.[0-9]+(\.[0-9]+)?' | head -n1)
[ -z "$ver" ] && { echo "UnrealIRCd tidak ditemukan di direktori ini"; exit 0; }
mod=$(./unrealircd module-status 2>/dev/null | grep -i 'labeled-response' | head -n1)
echo "Versi UnrealIRCd : $ver"
echo "Status modul     : ${mod:-labeled-response tidak terlihat dimuat}"
maj=${ver%%.*}
lowest=$(printf '%s\n%s\n' "$ver" "6.2.7.1" | sort -V | head -n1)
if [ "$maj" -lt 5 ]; then
  echo "HASIL: seri lama yang tidak diperiksa vendor. Migrasi ke seri 6."
elif [ "$maj" -eq 5 ]; then
  echo "HASIL: RENTAN dan tidak ada patch (seri 5 sudah EOL). Blacklist modul, lalu migrasi ke seri 6."
elif [ "$lowest" = "6.2.7.1" ]; then
  echo "HASIL: versi sudah memuat perbaikan."
elif echo "$mod" | grep -qi 'hot-patch'; then
  echo "HASIL: hot-patch terpasang. Tetap jadwalkan upgrade ke 6.2.7.1."
else
  echo "HASIL: RENTAN. Pasang hot-patch atau upgrade ke 6.2.7.1."
fi
One unpatched server is enough to expose the entire network, so run checks on all servers, including the hub.
How to update safely?
The quickest way is to install the hot-patch on all servers without restarting, then schedule a full upgrade to 6.2.7.1.
Step 1: quick mitigation
For series 6.0.0 to 6.2.7, install the official hot-patch bundle. Users are not disconnected because the server does not need to be restarted.
cd ~/unrealircd
./unrealircd hot-patch bundle-20261107

# verifikasi: baris labeled-response harus menunjukkan hot-patch
./unrealircd module-status | grep -i labeled-response
If the hot patch cannot be installed, the manager provides a temporary spamfilter rule that rejects invalid label tags. The rule only works if all servers are running 6.0.4 or later. Copy the exact text from the official UnrealIRCd announcement, then delete it once all servers are patched.
For the 5.x series, there is no patch. Add the following lines to each server's configuration, then restart (rehash alone is not enough):
# unrealircd.conf
blacklist-module "labeled-response";
Step 2: update and verify
cd ~/unrealircd
./unrealircd upgrade
./unrealircd restart

# verifikasi versi dan modul
./unrealircd version
./unrealircd module-status | grep -i labeled-response
Upgrade servers one by one, starting from the hub, so that the network remains connected. Hot-patches and spamfilters only close these loopholes and the issues the bundle covers. Upgrading to 6.2.7.1 is still necessary for all nine fixes to be installed permanently.
How to detect signs of abuse?
There is no official list of indicators yet, so detection is done by looking for operator actions that are not carried out by the operator. Check the following as of November 7, 2026:
- KILL, GLINE, or other server commands that do not match your IRCOp work log.
- Ban entire networks that come up without anyone even bothering to install them.
- Links between servers are broken or protocol errors occur at close times.
- Unexplained change in channel mode, ownership or ban list.
# sesuaikan lokasi log dengan konfigurasi Anda
cd ~/unrealircd/logs
grep -hiE "kill|gline|g-line|zline|shun" ircd.log* | tail -n 100

# putus-sambung link antarserver
grep -hiE "link|squit|server .* (closed|lost)" ircd.log* | tail -n 50
A failed experiment may leave no trace. If a temporary spamfilter is installed, the block record could be an indication of an attempt.
If you find signs of abuse?
- Patch all servers first so that the attack path is closed.
- Review and remove GLINE, ZLINE, and unknown tires.
- Check operator accounts, transfer passwords, and server-to-server link credentials. Replace when in doubt.
- Check important channels: owner, mode, and access list in services.
- Notify users of any outages or mass bans, so they know the cause.
Frequently asked questions
What is UnrealIRCd?
UnrealIRCd is open source IRC server software developed since 1999. Many community and internal chat networks use it because it is modular and easy to configure.
I only have one server, without links to other servers. Is it safe?
The server-authorized attack path does not apply to a single server. Keep 6.2.7.1 installed, as that release also patches eight other issues, including an IP address leak and several crashes.
Is a hot patch enough, or does an upgrade have to be done?
A hot-patch is enough to close this gap quickly without disconnecting the user. Upgrading to 6.2.7.1 is still recommended so that the fix persists after a server restart and the version is clear.
Does the attacker need an account or operator status?
No. Ordinary users who can connect to one of the servers are enough. That is the reason this gap is considered very serious by the management.
I'm still using UnrealIRCd 5. What should I do?
Blacklist module labeled-response on all servers then restart. After that, migrate to series 6, because series 5 has not received security fixes since July 1, 2023.
Also read about the other flaws that KEV hit this week: the Check Point Gaia flaw CVE-2026-123039, the OpenSSH sshole flaw in Alpine Linux, and the FreeSWITCH flaw CVE-2026-116779.
Source
- UnrealIRCd: 6.2.7.1 release and hot-patch announcement (November 7, 2026)
- CISA: Adds Two Known Exploited Vulnerabilities to Catalog (13 November 2026)
- The Hacker News: Attackers Exploit UnrealIRCd Flaw That Enables Server-Level Command Injection
- Ostorlab: UnrealIRCd Command Injection, Exploited in the Wild (CVE-2026-114713)
- OSV: note CVE-2026-114713 and CVSS vectors
Topics: #keamanan #cve #unrealircd #irc #cisa kev #server
About the author
Tim APIPedia — Tim Engineering APIPedia
Tim engineering di balik APIPedia yang membangun dan memelihara API data Indonesia - ongkir, OCR KTP, data wilayah, BMKG, hingga server MCP - dan menulis panduan integrasinya dari pengalaman langsung.